

SailPoint IdentityIQ-Engineer Premium Exam Engine pdf - Download Free Updated 201 Questions
Verified IdentityIQ-Engineer Bundle Real Exam Dumps PDF
SailPoint IdentityIQ-Engineer Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
NEW QUESTION # 120
Is this a benefit of using the Run Rule feature of the Debug-Object page?
Solution: It can be used to create/modify/delete SailPoint database objects.
- A. Yes
- B. No
Answer: B
Explanation:
The statement is false. The "Run Rule" feature on the Debug-Object page is not intended for creating, modifying, or deleting SailPoint database objects. Instead, it is used to execute specific rules for testing and debugging purposes. While it allows you to test the logic of a rule by running it in isolation, it does not directly manipulate database objects. For creating, modifying, or deleting database objects, administrators would typically use the appropriate IdentityIQ APIs or database scripts.
Reference:
SailPoint IdentityIQ Administration Guide (Debugging and Rule Management Sections) SailPoint IdentityIQ Developer Guide (Working with Rules and Debugging Tools)
NEW QUESTION # 121
A customer wants to make changes in their IdentitylQ user interface. Consider branding and other IdentitylQ Ul changes. Is this statement valid?
Solution: Primary and secondary colors are set through the IdentitylQ Configuration > Miscellaneous page.
- A. Yes
- B. No
Answer: B
Explanation:
The primary and secondary colors in the IdentityIQ user interface are not set through the IdentityIQ Configuration > Miscellaneous page. Instead, these colors are typically configured through the style.css or other custom CSS files that are part of the IdentityIQ UI customization process. Administrators can define and modify the color scheme, fonts, and other style elements by editing the relevant CSS files or using the Branding feature within IdentityIQ.
Therefore, the correct answer is B. No.
Reference:This information is based on the SailPoint IdentityIQ Branding Guide, which details how to modify the visual aspects of the UI, including colors, by editing CSS files rather than through the Miscellaneous settings.
NEW QUESTION # 122
Assuming that the policy violation owner has the necessary permissions, is this a valid option for the policy violation owner to use when acting on a policy violation of type ' Role SOD Policy?
Solution: Schedule Policy Composition Certification
- A. Yes
- B. No
Answer: B
Explanation:
In SailPoint IdentityIQ, when dealing with a policy violation of the type " Role Separation of Duties (SOD) Policy, " there are specific actions that the policy violation owner can take. These options typically include:
* Mitigate: Applying a mitigating control to the violation.
* Remediate: Addressing the violation by removing or altering access.
* Accept: Acknowledging the violation without making changes, which usually requires justification.
* Forward: Assigning the violation to another individual or group for resolution.
The option " Schedule Policy Composition Certification " is not a valid action for addressing a Role SOD Policy violation directly. The concept of scheduling a certification is related to periodic review processes, not immediate policy violation handling. Certification campaigns are scheduled and executed to review roles, entitlements, or policies, but this is not an action taken in response to a specific policy violation.
Thus, " Schedule Policy Composition Certification " is not an appropriate or valid option in this context, and the correct answer is B. No.
Reference:This explanation is corroborated by the SailPoint IdentityIQ Compliance Manager documentation, which outlines the various actions available to policy violation owners when responding to policy violations, including Role SOD policies. The documentation specifies the actions that can be taken, and scheduling a certification is not listed among them in this context.
NEW QUESTION # 123
The engineer is working on a workflow implementation.
After a form step, the workflow can transition to three steps:
Stop if the Reject (back) button is used,
Audit if the Approve (next) button is used and the field named comment is returned from the form to the workflow variable comment and has a value, Provision otherwise.
The engineer writes the transitions in XML code.
Is this a valid implementation?
Proposed Solution:
< Transition >
< Source >
if (!approved) return " Stop " ;
if (comment) return " Audit " ;
return " Provision " ;
< /Source >
< /Transition >
- A. Yes
- B. No
Answer: B
Explanation:
This proposed implementation is not valid as written. The logic is conceptually understandable, but the XML structure is not the correct IdentityIQ workflow transition pattern. In IdentityIQ workflows, transitions are normally declared using < Transition > elements with a destination, such as to= " StepName " , and optional conditional logic through a when expression or scripted evaluation. A raw < Source > block directly inside < Transition > returning destination names is not the standard structure for expressing multiple workflow routing paths after a form step. The engineer's requirement is to route to Stop when the reject/back action is used, route to Audit when approval occurs and the comment variable is populated, and route to Provision as the fallback. That should be implemented as separate transition definitions with explicit destination steps and conditions. The proposed XML does not properly bind the returned values to valid transition destinations in the expected workflow syntax. References/topics: IdentityIQ Engineer - workflow XML, transition elements, form step routing, BeanShell expressions, Business Process Editor.
NEW QUESTION # 124
The JVM Memory page on IdentitylQ displays the following information: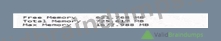
Solution: How much memory is currently allocated to the JVM heap?
Type your numerical response into the box below.
Answer:
Explanation:
725.617 MB
Explanation:
The " Total Memory " value displayed on the JVM Memory page indicates the amount of memory currently allocated to the JVM heap. In the image provided, the " Total Memory " is shown as 725.617 MB. This is the amount of memory that the JVM heap is currently using, meaning it has been allocated and is available for the JVM to use.
SailPoint IdentityIQ Performance Tuning and Monitoring Guide
SailPoint IdentityIQ Administration Guide (JVM and Memory Management Sections)
NEW QUESTION # 125
A bank is two years into an ongoing project to provide all access through roles. The bank is actively using roles and actively adding to their role model. They need to ensure that all roles include the correct entitlements.
Will this certification type achieve the goal?
Solution: Role Composition Certification
- A. Yes
- B. No
Answer: A
Explanation:
A Role Composition Certification is specifically designed to ensure that roles are composed correctly by reviewing the entitlements and other roles they aggregate. This certification allows reviewers to verify whether the roles include the appropriate entitlements based on business needs and compliance requirements.
Given that the bank's objective is to ensure that all roles include the correct entitlements, a Role Composition Certification is the most appropriate tool to achieve this goal. It allows for the comprehensive review and validation of roles and their associated entitlements, ensuring alignment with the overall access governance strategy.
Therefore, the correct answer is A. Yes.
NEW QUESTION # 126
Can the following be achieved via configuration of control variables in the out-of-the-box Lifecycle Manager (LCM) workflows?
Solution: Disable all notifications.
- A. Yes
- B. No
Answer: A
Explanation:
Yes, disabling all notifications can be achieved via configuration of control variables in the out-of-the-box Lifecycle Manager (LCM) workflows. In SailPoint IdentityIQ, most workflows, including those in LCM, use control variables to manage various settings, such as whether notifications should be sent. By setting the appropriate control variable (e.g., disabling email notifications) within the workflow configuration, you can effectively suppress all notifications related to that workflow.
Therefore, the correct answer is A. Yes.
NEW QUESTION # 127
Can the search type in Syslog be used to accomplish this result?
Solution: Identifying details of a system error presented in the Ul
- A. Yes
- B. No
Answer: A
Explanation:
Syslog can be used to identify the details of a system error presented in the UI. When a system error occurs, IdentityIQ typically logs detailed error messages, stack traces, and other relevant information to Syslog or other logging frameworks configured in the environment. By reviewing these logs, an administrator or engineer can identify and diagnose the specific error that was encountered in the UI.
SailPoint IdentityIQ Logging and Monitoring Guide
SailPoint IdentityIQ Administration Guide (Sections on Error Handling and Troubleshooting)
NEW QUESTION # 128
For a user who already has an account on an application and wants to be able to request access to a new account through Manage User Access, does this configuration need to be performed in Lifecycle Manager (LCM)?
Proposed Solution:
Select "Allow requesting new accounts" in the Manage Accounts QuickLink configuration for the user's QuickLink population.
- A. Yes
- B. No
Answer: A
Explanation:
Yes. If a user already has an account on an application and needs the ability to request an additional/new account through Manage User Access, the relevant LCM/QuickLink configuration must permit requesting new accounts. The proposed setting, "Allow requesting new accounts," is specifically aligned with that requirement. Manage User Access and Manage Accounts behavior is controlled through Lifecycle Manager quicklink and population configuration, which determines what actions are visible and available to eligible users. Without enabling new-account requests for the appropriate QuickLink population, the user may only be able to manage existing account access or request entitlements for current accounts, not initiate a new account request on that application. This setting must also align with the application's provisioning support and account creation policy. The configuration grants the UI/request capability; successful fulfillment still depends on application schema, create policy, approvals, and provisioning workflow. References/topics:
IdentityIQ Engineer - LCM, Manage User Access, Manage Accounts QuickLink, QuickLink population, new account request, provisioning policy.
NEW QUESTION # 129
Can the Environment tab under 'Administrator Console' be used to do the following task?
Proposed Solution:
Start/Stop a particular application server.
- A. Yes
- B. No
Answer: B
Explanation:
No. The Environment tab in the IdentityIQ Administrator Console is not used to start or stop a particular application server. Starting and stopping an application server is an infrastructure-level operation handled by the application-server platform, operating system service manager, container orchestration layer, or hosting environment. IdentityIQ can display environment and runtime information, but it does not replace WebLogic, Tomcat, JBoss/WildFly, systemd, Windows Services, Kubernetes, or other server-control mechanisms. This distinction matters because engineers must not assume IdentityIQ UI controls can manage the underlying Java application server lifecycle. The Environment area is for visibility and administrative inspection, not for controlling server process state. To restart or stop a node, the engineer must use the proper server administration tool and follow clustered-environment procedures to avoid disrupting tasks, workflow execution, aggregation, provisioning, or user sessions. References/topics: IdentityIQ Engineer - Administrator Console, Environment tab, application server administration, clustered deployment operations, runtime monitoring.
NEW QUESTION # 130
A client wants users who belong to an IdentitylQ workgroup named Management to be able to request entitlements and roles, but only for other users whose location attribute is the same as theirs.
Is this a population that will achieve the goal?
Solution: Create a quicklink population, set the membership match list to the IdentitylQ workgroup " Management, " and set " Who can members request for? " as report to the requester.
- A. Yes
- B. No
Answer: B
Explanation:
* The provided solution does not fulfill the client ' s requirement. Setting " Who can members request for? " to " report to the requester " only limits the request scope to users who directly report to the requester, which does not account for the location attribute. The goal is to restrict requests based on the location attribute, and this specific configuration does not consider that attribute. To achieve the desired behavior, the configuration should include logic that filters users based on the same location as the requester.
References:
SailPoint IdentityIQ Quicklink Population Configuration Guide
SailPoint IdentityIQ Advanced Population Management Guide
NEW QUESTION # 131
Is this a correct procedure for testing generated emails in a non-production system?
Solution: Change the Email Notification Type to POP3 under Global Settings > Configure IdentitylQ Settings > Mail Settings, run the test scenario. and verity if the emails were successfully delivered to mailboxes specified on Identity objects.
- A. Yes
- B. No
Answer: B
Explanation:
Changing the Email Notification Type to POP3 under Global Settings > Configure IdentityIQ Settings > Mail Settings is not a correct procedure for testing generated emails in a non-production system. POP3 is an email retrieval protocol, not a method for sending or redirecting email notifications from IdentityIQ. IdentityIQ requires an SMTP server to send emails, and POP3 is typically used by email clients to retrieve emails from a server, not by a server to send emails.
For testing purposes in a non-production environment, you would typically configure the SMTP server settings to either redirect emails to a specific testing mailbox or use a "Redirect to File" option, if available, to capture emails locally.
Thus, the correct answer is B. No.
NEW QUESTION # 132
Is the following statement about workflow step types and their usage true?
Proposed Solution:
A step with the attribute wait= " 1 " will cause the workflow to wait for at least one minute. The workflow will be revived on the next run of the Perform Maintenance Task, after the wait period is over.
- A. Yes
- B. No
Answer: A
Explanation:
Yes. In IdentityIQ workflow processing, a wait step is not simply a client-side pause or a frozen browser session. The workflow case is persisted and resumed after the wait condition has elapsed and the maintenance process revives eligible workflow cases. A wait= " 1 " attribute represents a minimum wait period, and the workflow does not necessarily resume at the exact instant the wait expires. It resumes when IdentityIQ's background maintenance processing detects that the wait period is over and advances the workflow. That is why the wording says "at least one minute" and "on the next run of the Perform Maintenance Task." This distinction matters operationally: workflow timing depends on both the configured wait value and the maintenance task schedule. Engineers should not use wait steps when exact real-time execution is required.
References/topics: IdentityIQ Engineer - workflow wait attribute, persisted workflow cases, Perform Maintenance task, background workflow resumption, workflow step behavior.
NEW QUESTION # 133
Assuming that the policy violation owner has the necessary permissions, is this a valid option for the policy violation owner to use when acting on a policy violation of type 'Role SOD Policy?
Solution: Schedule Policy Composition Certification
- A. Yes
- B. No
Answer: B
Explanation:
In SailPoint IdentityIQ, when dealing with a policy violation of the type "Role Separation of Duties (SOD) Policy," there are specific actions that the policy violation owner can take. These options typically include:
Mitigate: Applying a mitigating control to the violation.
Remediate: Addressing the violation by removing or altering access.
Accept: Acknowledging the violation without making changes, which usually requires justification.
Forward: Assigning the violation to another individual or group for resolution.
The option "Schedule Policy Composition Certification" is not a valid action for addressing a Role SOD Policy violation directly. The concept of scheduling a certification is related to periodic review processes, not immediate policy violation handling. Certification campaigns are scheduled and executed to review roles, entitlements, or policies, but this is not an action taken in response to a specific policy violation.
Thus, "Schedule Policy Composition Certification" is not an appropriate or valid option in this context, and the correct answer is B. No.
Reference:
This explanation is corroborated by the SailPoint IdentityIQ Compliance Manager documentation, which outlines the various actions available to policy violation owners when responding to policy violations, including Role SOD policies. The documentation specifies the actions that can be taken, and scheduling a certification is not listed among them in this context.
NEW QUESTION # 134
Is this a valid step to take when importing SailPoint XML file objects into IdentityIQ?
Proposed Solution:
Select the file from Global Settings > Import From File.
- A. Yes
- B. No
Answer: A
Explanation:
Yes. Importing SailPoint XML objects can be performed through supported IdentityIQ import mechanisms, and using the user interface path Global Settings > Import From File is a valid approach for importing XML object definitions. XML imports are commonly used to move IdentityIQ configuration objects such as rules, workflows, applications, roles, policies, email templates, task definitions, and other SailPoint objects between environments. Engineers may also use the IdentityIQ console for imports, especially for larger or automated deployments, but the existence of the console method does not make the UI method invalid. The proposed solution is specifically asking whether selecting a file through Global Settings > Import From File is a valid step, and it is. The important caution is that imported XML should be reviewed carefully because object names, IDs, references, and environment-specific values can affect behavior after import. References/topics:
IdentityIQ Engineer - XML object import/export, Global Settings import, configuration migration, deployment management.
NEW QUESTION # 135
Is this statement true about identitylQ ' s syslog event storage?
Solution: Both logging and auditing can have a negative influence on performance. Logging and auditing both require extra function calls within The application and will generate data that will need to be stored.
- A. Yes
- B. No
Answer: A
Explanation:
Yes, the statement is true. Both logging and auditing in SailPoint IdentityIQ can have a negative influence on performance because they involve additional function calls within the application. These processes generate data that needs to be stored, which can impact performance if not managed properly. Extensive logging and auditing, particularly at high levels of detail, can lead to increased I/O and storage usage, potentially slowing down system operations.
SailPoint IdentityIQ Performance Tuning Guide
SailPoint IdentityIQ Logging and Auditing Guide (Impact on Performance)
NEW QUESTION # 136
Is this a true statement about localization support in IdentitylQ?
Solution: Message files may be added to support additional languages, but the out-of-the-box supplied message files cannot be modified.
- A. Yes
- B. No
Answer: B
Explanation:
The statement is false. In SailPoint IdentityIQ, while message files may indeed be added to support additional languages, the out-of-the-box supplied message files can also be modified. Administrators can customize these message files to adapt the text in the user interface to better suit the organization's needs. This includes modifying existing translations or adding custom messages to meet specific requirements.
Reference:
SailPoint IdentityIQ Localization Guide
SailPoint IdentityIQ Configuration Guide (Customization of Message Files)
NEW QUESTION # 137
Assuming that the policy violation owner has the necessary permissions, is this a valid option for the policy violation owner to use when acting on a policy violation of type ' Account Policy ' ?
Proposed Solution:
Schedule Policy Composition Certification
- A. Yes
- B. No
Answer: B
Explanation:
Schedule Policy Composition Certification is not a valid action for handling an individual Account Policy violation. A policy violation owner acts on a violation by making a decision about that violation: allow it, remediate it, mitigate it, or route it according to configured compliance processes. A Policy Composition Certification is a separate governance activity used to review the construction or definition of policies; it is not an immediate action available on a single violation record. The proposed solution also mismatches the policy type. The stem concerns an Account Policy violation, which typically relates to account-count or account-condition rules, not policy-composition review. The Word bank separately identifies Account policies as limiting the number of accounts a user can have on a system. Scheduling a certification might help long-term governance hygiene, but it does not dispose of the current policy violation. References/topics:
IdentityIQ Engineer - Account Policy violations, violation owner actions, certification types, policy composition certification, compliance remediation workflow.
NEW QUESTION # 138
A customer wants to make changes in their IdentitylQ user interface. Consider branding and other IdentitylQ Ul changes. Is this statement valid?
Solution: The sets of columns displayed in most tables in the IdentitylQ user interface are controlled by entries in the ColumnConfig elements of the UlConfig object.
- A. Yes
- B. No
Answer: A
Explanation:
Yes, the sets of columns displayed in most tables in the IdentityIQ user interface are controlled by entries in the ColumnConfig elements of the UIConfig object. The UIConfig object in IdentityIQ is responsible for defining various aspects of the user interface, including the configuration of columns that are displayed in tables throughout the application. By modifying the ColumnConfig elements within this object, administrators can customize which columns appear in specific tables, including their order, visibility, and labels.
Therefore, the correct answer is A. Yes.
Reference:This information is supported by the SailPoint IdentityIQ Configuration Guide, which outlines how UIConfig and ColumnConfig elements are used to control the display of data in the user interface.
NEW QUESTION # 139
An engineer needs to trigger a workflow when a Division attribute changes from IT to Senior IT, but only when the user is a manager.
Is this a valid process that the engineer could use to launch a workflow for a lifecycle event?
Proposed Solution:
Create a trigger with an event type of rule that checks if the previous value is IT and the new value is Senior IT, and return true if the managerStatus on the user ' s Identity Cube is true.
- A. Yes
- B. No
Answer: A
Explanation:
This is a valid process. The requirement has two parts: detect a specific Division transition and confirm that the identity is a manager. A rule-based lifecycle event trigger is appropriate when the condition is more complex than a simple single-attribute check. The rule can inspect the previous and new values of the Division attribute and return true only when the value changes from IT to Senior IT. It can also evaluate the identity's managerStatus value on the Identity Cube to confirm that the user is a manager. Returning true from the rule allows IdentityIQ to launch the associated workflow only for identities that satisfy both conditions.
This approach avoids the flaw of triggering on the wrong attribute and gives the engineer precise control over the lifecycle event condition. The key is that the rule must be written against the correct before-and-after identity data available during refresh or lifecycle-event evaluation. References/topics: IdentityIQ Engineer - rule-based lifecycle triggers, identity attribute changes, Identity Cube attributes, workflow launch rules, mover-event logic.
NEW QUESTION # 140
A client wants users who belong to an IdentitylQ workgroup named Management to be able to request entitlements and roles, but only for other users whose location attribute is the same as theirs.
Is this a population that will achieve the goal?
Solution: Create a quicklink population, set the membership match list to "All," and set "Who can members request for?'' as share attributes with the requester, with the attribute set to location.'
- A. Yes
- B. No
Answer: A
Explanation:
This solution correctly addresses the client's requirement. By setting the membership match list to "All" and configuring "Who can members request for?" as "share attributes with the requester," with the attribute set to location, the system ensures that users in the "Management" workgroup can only request roles and entitlements for other users who share the same location. This setup effectively filters based on the location attribute, aligning with the client's needs.
Reference:
SailPoint IdentityIQ Quicklink Population Configuration Guide
SailPoint IdentityIQ Attribute-Based Access Control Guide
NEW QUESTION # 141
Can the following be achieved via configuration of control variables in the out-of-the-box Lifecycle Manager (LCM) workflows?
Solution: Disable all notifications.
- A. Yes
- B. No
Answer: A
Explanation:
Yes, disabling all notifications can be achieved via configuration of control variables in the out-of-the-box Lifecycle Manager (LCM) workflows. In SailPoint IdentityIQ, most workflows, including those in LCM, use control variables to manage various settings, such as whether notifications should be sent. By setting the appropriate control variable (e.g., disabling email notifications) within the workflow configuration, you can effectively suppress all notifications related to that workflow.
Therefore, the correct answer is A. Yes.
Reference: This answer is based on the SailPoint IdentityIQ Workflow Guide, which explains how control variables can be configured in LCM workflows to manage behavior, including enabling or disabling notifications.
NEW QUESTION # 142
......
Pass Your SailPoint Exam with IdentityIQ-Engineer Exam Dumps: https://www.validbraindumps.com/IdentityIQ-Engineer-exam-prep.html
IdentityIQ-Engineer Dumps PDF New [2026] Ultimate Study Guide: https://drive.google.com/open?id=1tYWWtnc7-I-fKfmirdAdzt2xmYMs1fjG