

2025 Latest JN0-683 DUMPS Q&As with Explanations Verified & Correct Answers
JN0-683 dumps Exam Material with 67 Questions
NEW QUESTION # 38
Exhibit.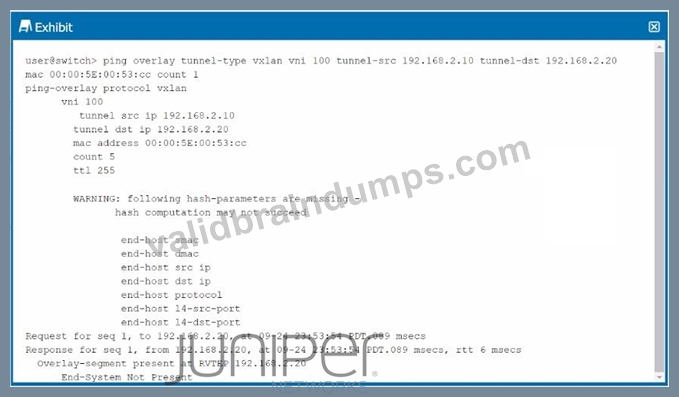
Referring tothe exhibit, which statement is correct?
- A. The MAC address is unknown and not in the forwarding table of the remote VTEP.
- B. The remote VTEP is not responding.
- C. The MAC address is known but not reachable by the remote VTEP
- D. VNI 100 is not configured on the remote VTEP.
Answer: A
Explanation:
* Analyzing the Exhibit Output:
* The command ping overlay tunnel-type vxlan is used to test the VXLAN tunnel between two VTEPs (VXLAN Tunnel Endpoints). The output shows a warning about missing hash parameters, but more importantly, it displays the result: End-System Not Present.
* Understanding the Response:
* The message End-System Not Present indicates that the remote VTEP (192.168.2.20) did not find the MAC address 00:00:5E:00:53:CC in its forwarding table. This typically means that the MAC address is unknown to the remote VTEP, and as a result, it could not forward the packet to the intended destination.
Conclusion:
* Option B:Correct-The MAC address is unknown and is not in the forwarding table of the remote VTEP, which is why the system reports that the "End-System" is not present.
NEW QUESTION # 39
You are asked to set up an IP fabric thatsupports Al or ML workloads. You have chosen to use lossless Ethernet in this scenario, which statement is correct about congestion management?
- A. ECN marks packets based on WRED settings.
- B. Only the source and destination devices need ECN enabled.
- C. ECN is negotiated only among the switches that make up the IP fabric for each queue.
- D. The switch experiencing the congestion notifies the source device.
Answer: D
Explanation:
* Understanding Lossless Ethernet and Congestion Management:
* Lossless Ethernet is crucial for AI and ML workloads, where packet loss can significantly degrade performance. To implement lossless Ethernet, congestion management protocols like ECN (Explicit Congestion Notification) are used.
* Role of ECN in Congestion Management:
* Option A:In an IP fabric that supports lossless Ethernet, when a switch experiences congestion, it can mark packets using ECN. This marking notifies the source device of the congestion, allowing the source to reduce its transmission rate, thereby preventing packet loss.
Conclusion:
* Option A:Correct-The switch experiencing congestion notifies the source device via ECN marking.
NEW QUESTION # 40
You are asked to interconnect two of your company's data centers across the IP backbone. Both data centers have their own unique IP space and do not require any bridging. In this scenario, which two actions would accomplish this task? (Choose two.)
- A. Configure peering for EVPN between all leaf nodes within each data center.
- B. Configure a Type 2 EVPN route for each unique prefix.
- C. Configure peering for EVPN between border leaf nodes in each data center.
- D. Configure a Type 5 EVPN route for each unique prefix.
Answer: C,D
Explanation:
* Interconnecting Data Centers:
* The scenario requires interconnecting two data centers with unique IP spaces across an IP backbone. The key point is that bridging is not required, so Layer 3 routing methods must be used.
* EVPN Configuration:
* Option B:Establishing EVPN peering between the border leaf nodes in each data center is the most appropriate solution as it allows for exchanging routing information between the two data centers. This ensures that the routes are properly distributed without the need for L2 bridging.
* Option C:Configuring Type 5 EVPN routes is necessary for advertising IP prefixes (Layer 3 routes) across the EVPN. Type 5 routes allow for the exchange of IP prefixes between the two data centers, enabling the necessary routing functionality without the need for bridging.
Conclusion:
* Option B:Correct-Peering between border leaf nodes sets up the necessary route exchange between data centers.
* Option C:Correct-Type 5 EVPN routes are essential for exchanging Layer 3 prefixes between data centers.
NEW QUESTION # 41
You want to ensure thatVXLAN traffic from the xe-0/0/12 interlace is being encapsulatedby logical vlep.
32770 and sent to a remote leaf device in this scenario, which command would you use to verify that traffic is flowing?
- A. show interfaces terse vtep.32770 statistics
- B. show interface terse vtep.32770
- C. monitor traffic interface xe-0/0/12
- D. show interfaces vtep.32770 detail
Answer: A
Explanation:
* VXLAN Traffic Verification:
* To ensure VXLAN traffic from the xe-0/0/12 interface is correctly encapsulated by the logical vtep.32770 and sent to a remote leaf device, it is essential to monitor the relevant interface statistics.
* The command show interfaces terse vtep.32770 statistics provides a concise overview of the traffic statistics for the specific VTEP interface, which can help verify whether traffic is being correctly encapsulated and transmitted.
* Explanation:
* This command is particularly useful for quickly checking the traffic counters and identifying any potential issues with VXLAN encapsulation or transmission.
* It allows you to confirm that traffic is flowing as expected, by checking the transmitted and received packet counters.
Data Center References:
* Monitoring interface statistics is a crucial step in troubleshooting and validating network traffic, particularly in complex overlay environments like EVPN-VXLAN.
NEW QUESTION # 42
You are deploying an IP fabric using EBGP and notice that your leaf devices areadvertising and receiving all the routes. However, the routes are not installed in the routing table and are marked as hidden.
Which two statements describe how to solve the issue? (Choose two.)
- A. You need to configure loops 2.
- B. You need to configure multipath multiple-as.
- C. You need to configure as-override.
- D. You need to configure a next-hop self policy.
Answer: B,D
NEW QUESTION # 43
A local VTEP has two ECMP paths to a remote VTEP
Which two statements are correctwhen load balancing is enabled in this scenario? (Choose two.)
- A. The inner packet fields are used in the hash for load balancing.
- B. The inner packet fields are not used in the hash for load balancing.
- C. The source port in the UDP header is used to load balance VXLAN traffic.
- D. The destination port in the UDP header is used to load balance VXLAN traffic.
Answer: A,C
Explanation:
* Load Balancing in VXLAN:
* VXLAN uses UDP encapsulation to transport Layer 2 frames over an IP network. For load balancing across Equal-Cost Multi-Path (ECMP) links, various fields in the packet can be used to ensure even distribution of traffic.
* Key Load Balancing Fields:
* C. The source port in the UDP header is used to load balance VXLAN traffic:This is correct.
The source UDP port in the VXLAN packet is typically calculated based on a hash of the inner packet's fields. This makes the source port vary between packets, enabling effective load balancing across multiple paths.
* D. The inner packet fields are used in the hash for load balancing:This is also correct. Fields such as the source and destination IP addresses, source and destination MACaddresses, and possibly even higher-layer protocol information from the inner packet can be used to generate the hash that determines the ECMP path.
* Incorrect Statements:
* A. The inner packet fields are not used in the hash for load balancing:This is incorrect as the inner packet fields are indeed critical for generating the hash used in load balancing.
* B. The destination port in the UDP header is used to load balance VXLAN traffic:This is incorrect because the destination UDP port in VXLAN packets is typically fixed (e.g., port 4789 for VXLAN), and therefore cannot be used for effective load balancing.
Data Center References:
* Effective load balancing in VXLAN is crucial for ensuring high throughput and avoiding congestion on specific links. By using a combination of the source UDP port and inner packet fields, the network can distribute traffic evenly across available paths.
NEW QUESTION # 44
Exhibit.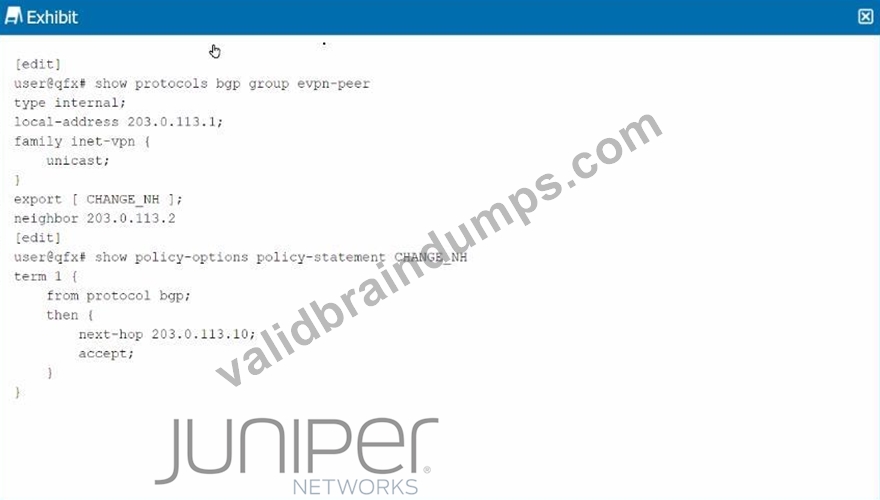
Given the configuration shown in the exhibit, why has the next hop remained the same for the EVPN routes advertised to the peer 203.0.113.2?
- A. The export policy is incorrectly configured.
- B. EVPN routes cannot have the next hop changed.
- C. The vpn-apply-export parameter must be applied to this peer.
- D. The vrf-export parameter must be applied.
Answer: C
Explanation:
* Understanding the Configuration:
* The configuration shown in the exhibit involves an EVPN (Ethernet VPN) setup using BGP as the routing protocol. The export policy named CHANGE_NH is applied to the BGP group evpn- peer, which includes a rule to change the next hop for routes that match the policy.
* Issue with Next Hop Not Changing:
* The policy CHANGE_NH is correctly configured to change the next hop to 203.0.113.10 for the matching routes. However, the next hop remains unchanged when advertising EVPN routes to the peer 203.0.113.2.
* Reason for the Issue:
* In Junos OS, when exporting routes for VPNs (including EVPN), the next-hop change defined in a policy will not take effect unless the vpn-apply-export parameter is used inthe BGP configuration. This parameter ensures that the export policy is applied specifically to VPN routes.
* The vpn-apply-export parameter must be included to apply the next-hop change to EVPN routes.
* Correct Answer Explanation:
* D. The vpn-apply-export parameter must be applied to this peer:This is the correct solution because the next hop in EVPN routes won't be altered without this parameter in the BGP configuration. It instructs the BGP process to apply the export policy to the EVPN routes.
Data Center References:
* This behavior is standard in EVPN deployments with Juniper Networks devices, where the export policies applied to VPN routes require explicit invocation using vpn-apply-export to take effect.
NEW QUESTION # 45
Exhibit.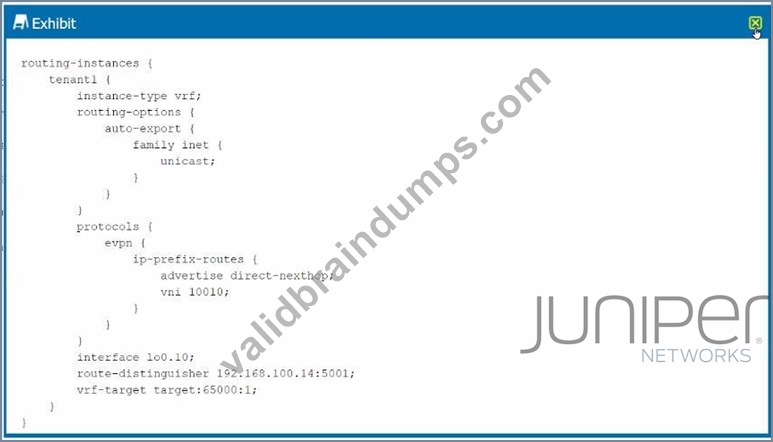
You want to enable the border leaf device to send Type 5 routes of local networks to the border leaf device in another data center. What must be changed to the configuration shown in the exhibit to satisfy this requirement?
- A. Move vrf-target target: 65000:1 to the evpn hierarchy.
- B. Add a VLAN configuration with an 13-interface to the tenant1 routing instance.
- C. Add encapsulation vxlan to the evpn hierarchy.
- D. Change: 5001 in the route-distinguisher to : 10010.
Answer: A
Explanation:
In this scenario, you want the border leaf device to advertise Type 5 EVPN routes to another border leaf in a different data center. Type 5 routes in EVPN are used to advertise IP prefixes, which means that for proper route advertisement, you need to configure the correct settings within the evpn hierarchy.
Step-by-Step Analysis:
* Understanding EVPN Type 5 Routes:
* EVPN Type 5 routes are used to advertise IP prefixes across EVPN instances, which allow different data centers or networks to exchange routing information effectively.
* VRF Target Setting:
* The vrf-target configuration is crucial because it defines the export and import policies for the VRF within the EVPN instance. For EVPN Type 5 routes to be advertised to other border leaf devices, the vrf-target needs to be correctly configured under the evpn hierarchy, not just within the routing instance.
Command to solve this:
move vrf-target target:65000:1 to evpn
* Other Options:
* Option B:Adding a VLAN configuration would not address the requirement to advertise Type 5 routes.
* Option C:Adding VXLAN encapsulation may be necessary for other scenarios but does not directly address the Type 5 route advertisement.
* Option D:Changing the route-distinguisher will differentiate routes but does not impact the advertisement of Type 5 routes to other data centers.
By moving the vrf-target to the evpn hierarchy, you enable the proper route advertisement, ensuring that the Type 5 routes for local networks are shared with other data center border leaf devices. This is aligned with best practices for multi-data center EVPN implementations, which emphasize the correct placement of routing policies within the EVPN configuration.
NEW QUESTION # 46
Exhibit.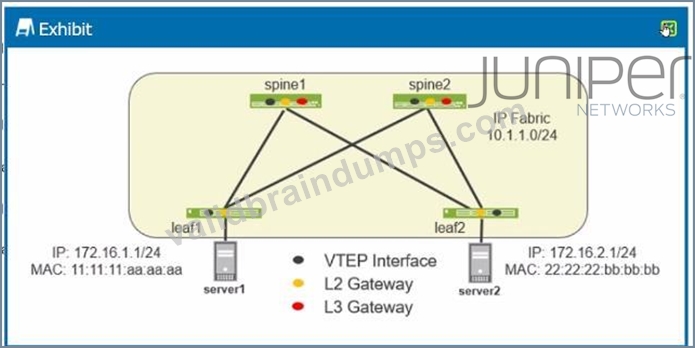
You have implemented an EVPN-VXLAN data center. Device served must be able to communicate with device server2.
Referring to the exhibit, which two statements are correct? (Choose two.)
- A. An IRB interface must be configured on spinel and spine2.
- B. Traffic from server! to server2 will transit the VXLAN tunnel between leaf1 and Ieaf2.
- C. Traffic from server1 to server2 will transit a VXLAN tunnel to spinel or spine2. then a VXLAN tunnel from spinel or spine2 to Ieaf2.
- D. An IRB Interface must be configured on leaf1 and Ieaf2.
Answer: B,D
Explanation:
* Understanding the Exhibit Setup:
* The network diagram shows an EVPN-VXLAN setup, a common design for modern data centers enabling Layer 2 and Layer 3 services over an IP fabric.
* Leaf1 and Leaf2 are the leaf switches connected to Server1 and Server2, respectively, with each server in a different subnet (172.16.1.0/24 and 172.16.2.0/24).
* Spine1 and Spine2 are part of the IP fabric, interconnecting the leaf switches.
* EVPN-VXLAN Basics:
* EVPN (Ethernet VPN) provides Layer 2 and Layer 3 VPN services using MP-BGP.
* VXLAN (Virtual Extensible LAN) encapsulates Layer 2 frames into Layer 3 packets for transmission across an IP network.
* VTEP (VXLAN Tunnel Endpoint) interfaces on leaf devices handle VXLAN encapsulation and decapsulation.
* Integrated Routing and Bridging (IRB):
* IRB interfaces are required on leaf1 and leaf2 (where the endpoints are directly connected) to route between different subnets (in this case, between 172.16.1.0/24 and 172.16.2.0/24).
* The IRB interfaces provide the necessary L3 gateway functions for inter-subnet communication.
* Traffic Flow Analysis:
* Traffic from Server1 (172.16.1.1) destined for Server2 (172.16.2.1) must traverse from leaf1 to leaf2.
* The traffic will be VXLAN encapsulated on leaf1, sent over the IP fabric, and decapsulated on leaf2.
* Since the communication is between different subnets, the IRB interfaces on leaf1 and leaf2 are crucial for routing the traffic correctly.
* Correct Statements:
* C. An IRB Interface must be configured on leaf1 and leaf2:This is necessary to perform the inter-subnet routing for traffic between Server1 and Server2.
* D. Traffic from server1 to server2 will transit the VXLAN tunnel between leaf1 and leaf2:
This describes the correct VXLAN operation where the traffic is encapsulated by leaf1 and decapsulated by leaf2.
Data Center References:
* In EVPN-VXLAN architectures, the leaf switches often handle both Layer 2 switching and Layer 3 routing via IRB interfaces. This allows for efficient routing within the data center fabric without the need to involve the spine switches for every routing decision.
* The described traffic flow aligns with standard EVPN-VXLAN designs, where direct VXLAN tunnels between leaf switches enable seamless and scalable communication across a data center network.
NEW QUESTION # 47
You want to provide a OCI that keeps each data center routing domain isolated, while also supporting translation of VNIs. Which DCI scheme allows these features?
- A. over the top (OTT) with VNI translation enabled
- B. MPLS DCI label exchange
- C. over the top (OTT) with proxy gateways
- D. VXLAN stitching
Answer: D
Explanation:
* Understanding DCI (Data Center Interconnect) Schemes:
* DCI schemes are used to connect multiple data centers, enabling seamless communication and resource sharing between them. The choice of DCI depends on the specific requirements, such as isolation, VNI translation, or routing domain separation.
* VXLAN Stitching:
* VXLAN stitching involves connecting multiple VXLAN segments, allowing VNIs (VXLAN Network Identifiers) from different segments to communicate with each other while maintaining separate routing domains.
* This approach is particularly effective for keeping routing domains isolated while supporting VNI translation, making it ideal for scenarios where you need to connect different data centers or networks without merging their control planes.
* Other Options:
* A. MPLS DCI label exchange:This option typically focuses on MPLS-based interconnections and does not inherently support VNI translation or isolation in the context of VXLAN.
* B. Over the top (OTT) with VNI translation enabled:This could support VNI translation but does not inherently ensure routing domain isolation.
* D. Over the top (OTT) with proxy gateways:This typically involves using external gateways for traffic routing and may not directly support VNI translation or isolation in the same way as VXLAN stitching.
Data Center References:
* VXLAN stitching is a powerful method in multi-data center environments, allowing for flexibility in connecting various VXLAN segments while preserving network isolation and supporting complex interconnect requirements.
NEW QUESTION # 48
Which two statements are true about EVPN routes for Data Center Interconnect? (Choose two.)
- A. Type 5 EVPN routes do not require a VXLAN tunnel to the protocol next hop.
- B. Type 2 EVPN routes do not require a VXLAN tunnel to the protocol next hop.
- C. Type 5 EVPN routes require a VXLAN tunnel to the protocol next hop.
- D. Type 2 EVPN routes require a VXLAN tunnel to the protocol next hop.
Answer: A,B
Explanation:
* Type 2 EVPN Routes:
* Type 2 routesadvertise MAC addresses within an EVPN instance and are used primarily for Layer 2 bridging. These routes do not require a VXLAN tunnel to the protocol next hop because they operate within the same Layer 2 domain.
* Type 5 EVPN Routes:
* Type 5 routesare used to advertise IP prefixes (Layer 3 routes) within EVPN. Similar to Type 2 routes, they do not require a VXLAN tunnel to the protocol next hop because they represent L3 routes, which are managed at the routing layer without the need for VXLAN encapsulation.
Conclusion:
* Option B:Correct-Type 2 routes do not need a VXLAN tunnel to the next hop, as they are used for Layer 2.
* Option D:Correct-Type 5 routes also do not need a VXLAN tunnel because they operate at Layer 3, handling IP prefixes.
NEW QUESTION # 49
You are selling up an EVPN-VXLAN architecture (or your new data center. thisinitial deployment will be less than 50 switches: however, it could scale up to 250 switches over time supporting 1024 VLANs. You are still deciding whether to use symmetric or asymmetric routing.
In this scenario, which two statements are correct? (Choose two.)
- A. Symmetric routing supports higher scaling numbers.
- B. Asymmetric routing is easier lo monitor because of the transit VNI.
- C. Symmetric routing needs an extra VLAN with an IRB interface for each L3 VRF instance.
- D. Asymmetric routing routes traffic on the egress switch.
Answer: A,D
Explanation:
* Symmetric vs. Asymmetric Routing in EVPN-VXLAN:
* Symmetric Routing:Traffic enters and exits the VXLAN network through the same VTEP, regardless of the source or destination. This approach simplifies routing decisions, especially in large networks, and is generally more scalable.
* Asymmetric Routing:The routing occurs on the egress VTEP. This method can be simpler to deploy in smaller environments but becomes complex as the network scales, particularly with larger numbers of VNIs and VLANs.
* Correct Statements:
* C. Symmetric routing supports higher scaling numbers:Symmetric routing is preferred in larger EVPN-VXLAN deployments because it centralizes routing decisions, which can be more easily managed and scaled.
* D. Asymmetric routing routes traffic on the egress switch:This is accurate, as asymmetric routing means the routing decision is made at the final hop, i.e., the egress VTEP before the traffic reaches its destination.
* Incorrect Statements:
* A. Symmetric routing needs an extra VLAN with an IRB interface for each L3 VRF instance:This is not accurate. Symmetric routing does not require an extra VLAN per VRF; rather, it uses the same VLAN/VNI across the network, simplifying routing and VLAN management.
* B. Asymmetric routing is easier to monitor because of the transit VNI:Asymmetric routing is not necessarily easier to monitor; in fact, it can add complexity due to the split routing logic between ingress and egress points.
Data Center References:
* The choice between symmetric and asymmetric routing in an EVPN-VXLAN environment depends on network size, complexity, and specific operational requirements. Symmetric routing is generally more scalable and easier to manage in large-scale deployments.
NEW QUESTION # 50
Exhibit.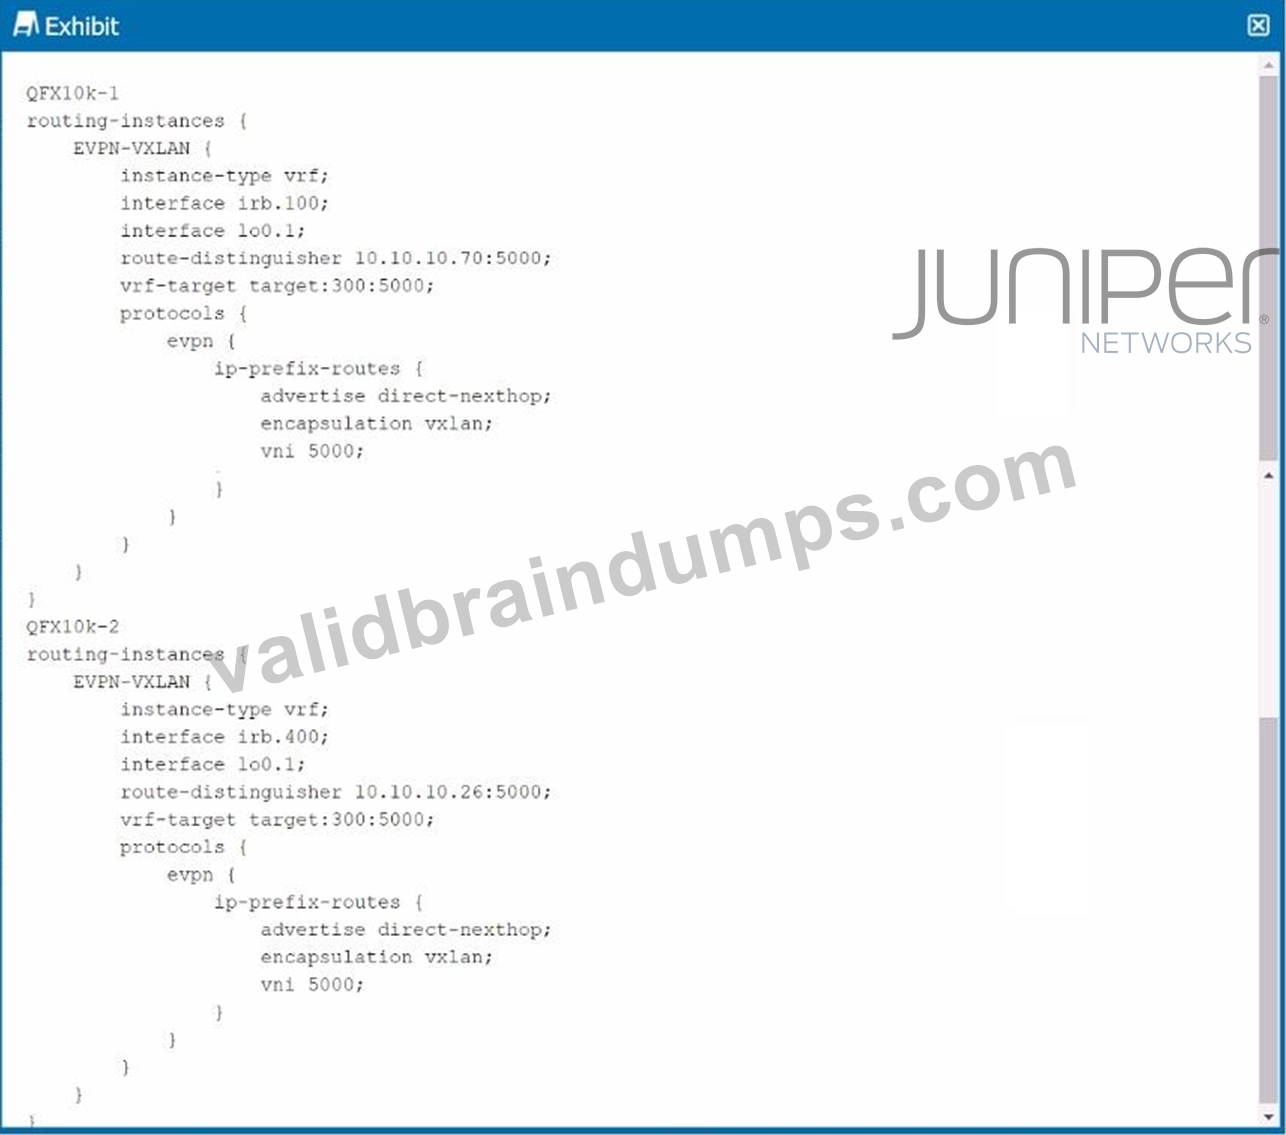
You have a sample configuration for connecting two sites through EVPN-VXLAN by exchanging IP prefix routes.
Referring to the exhibit, which two statements regarding the configuration are true? {Choose two.)
- A. The VNI should be unique on all devices for each customer site.
- B. The VNI must match on all devices for the same customer.
- C. The advertise direct-nexthop option enables the receiver to resolve the next-hop route using only information carried in the Type 5 route.
- D. The advertise direct-nexthop option enables the receiver to resolve the next-hop route using only information carried in the Type 2 route.
Answer: B,C
Explanation:
EVPN-VXLAN Configuration:
* The configuration provided in the exhibit shows an EVPN-VXLAN setup where IP prefix routes are exchanged between two sites. The advertise direct-nexthop option and the VNI (Virtual Network Identifier) settings are crucial in this context.
Advertise Direct-Nexthop:
* Option A:The advertise direct-nexthop option ensures that the next-hop route is resolved using only the information carried in the EVPN Type 5 route. Type 5 routes are used for IP prefix advertisement in EVPN, which is key to enabling Layer 3 interconnectivity between different VXLAN segments.
VNI Consistency:
* Option C:For the same customer across different devices, the VNI must be consistent. This consistency ensures that all devices can correctly map traffic to the appropriate VXLAN segment, maintaining seamless Layer 2 and Layer 3 connectivity.
NEW QUESTION # 51
You are asked for TX and RX traffic statistics for each interface to which an application server is attached.
The statistics need to be reported every five seconds. Using the Junos default settings, which telemetry method would accomplish this request?
- A. gNMI
- B. OpenConfig
- C. SNMP
- D. Native Sensors
Answer: D
Explanation:
* Telemetry Methods in Junos:
* Telemetry is used to collect and report data from network devices. For high-frequency statistics reporting, such as every five seconds, you need a telemetry method that supports this level of granularity and real-time monitoring.
* Junos Native Sensors:
* Option C:Native Sensors in Junos provide detailed, high-frequency telemetry data, including TX and RX traffic statistics for interfaces. They are designed to offer real-time monitoring with customizable sampling intervals, making them ideal for the five-second reporting requirement.
Conclusion:
* Option C:Correct-Native Sensors in Junos are capable of providing the required high-frequency telemetry data every five seconds.
NEW QUESTION # 52
Which three statements are correct about VXLAN control planes? (Choose three.)
- A. EVPN enables fast convergence and updates.
- B. Both multicast and EVPN can facilitate MAC learning.
- C. Multicast does not require as many resources.
- D. EVPN is inefficient and does not scale well.
- E. Multicast is not agile and requires manual VNI mapping.
Answer: A,B,C
Explanation:
* VXLAN Control Planes:
* VXLAN (Virtual Extensible LAN) uses different control planes to handle MAC learning and traffic forwarding. The control planes include multicast and EVPN (Ethernet VPN).
* Multicast and EVPN Comparison:
* Option B:Both multicast and EVPN can be used for MAC learning in a VXLAN environment.
Multicast is a more traditional approach, while EVPN is more advanced and supports distributed MAC learning.
* Option D:EVPN offers benefits such as fast convergence and rapid updates, making it more efficient and scalable for modern data center environments.
* Option E:Multicast does not require as many resources because it relies on traditional Layer 3 multicast mechanisms to distribute broadcast, unknown unicast, and multicast (BUM) traffic.
However, it can be less flexible and less scalable compared to EVPN.
Conclusion:
* Option B:Correct-Both control planes facilitate MAC learning.
* Option D:Correct-EVPN provides fast convergence and updates.
* Option E:Correct-Multicast is resource-efficient but less flexible.
NEW QUESTION # 53
You manage an IP fabric with an EVPN-VXLAN overlay. You have multiple tenants separated using multiple unique VRF instances. You want to determine the routing information that belongs in each routing instance's routing table.
In this scenario, which property is used for this purpose?
- A. the VRF target community
- B. the routing instance type
- C. the route distinguisher value
- D. the VRF table label
Answer: C
Explanation:
* Understanding VRF and Routing Instances:
* In an EVPN-VXLAN overlay network, multiple tenants are separated using unique VRF (Virtual Routing and Forwarding) instances. Each VRF instance maintains its own routing table, allowing for isolated routing domains within the same network infrastructure.
* Role of Route Distinguisher:
* Route Distinguisher (RD):The RD is a unique identifier used in MPLS and EVPN environments to distinguish routes belonging to different VRFs. The RD is prepended to the IP address in the route advertisement, ensuring that routes from different tenants remain unique even if they use the same IP address range.
* Correct Property:
* D. the route distinguisher value:This is the correct answer because the RD is crucial in determining which routing information belongs to which VRF instance. It ensures that each VRF' s routing table only contains relevant routes, maintaining isolation between tenants.
Data Center References:
* The RD is a key element in MPLS and EVPN-based multi-tenant environments, ensuring proper routing segregation and isolation for different VRFs within the data center fabric.
NEW QUESTION # 54
Exhibit.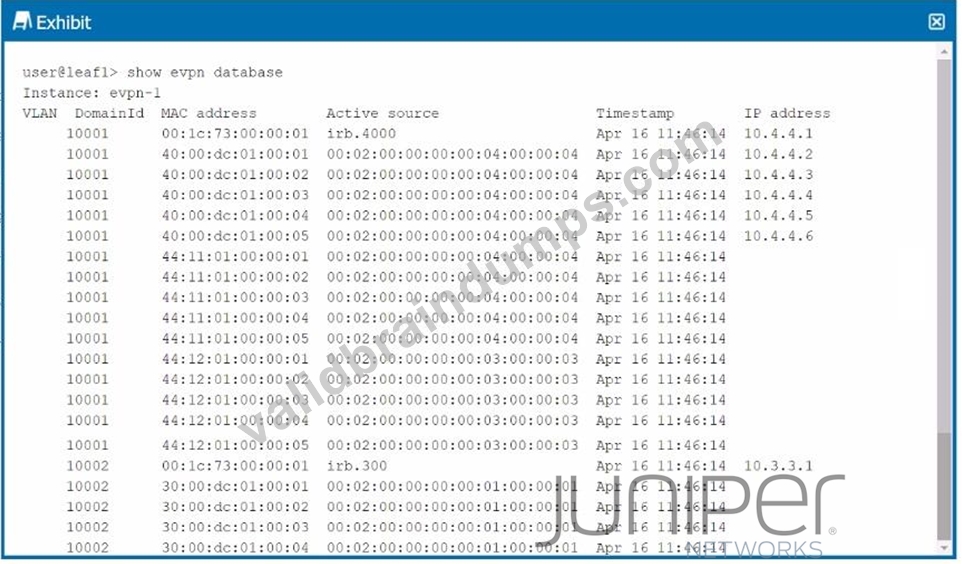
The exhibit shows the truncated output of the show evpn database command.
Given this output, which two statements are correct about the host with MAC address 40:00:dc:01:00:04?
(Choose two.)
- A. The host is assigned IP address 10.4.4.5.
- B. The host is originating from irb.300.
- C. The host is located on VN110002.
- D. The host is originating from an ESI LAG.
Answer: A,D
Explanation:
* Understanding the Output:
* The show evpn database command output shows the MAC address, VLAN, active source, timestamp, and IP address associated with various hosts in the EVPN instance.
* Analysis of the MAC Address:
* Option A:The MAC address 40:00:dc:01:00:04 is associated with the IP address 10.4.4.5, as indicated by the output in the IP address column. This confirms that this host has been assigned the IP 10.4.4.5.
* Option D:The active source for the MAC address 40:00:dc:01:00:04 is listed as 00:02:00:00:00:
04:00:04:00:00:04:00:04, which indicates that the host is connected via an ESI (Ethernet Segment Identifier) LAG (Link Aggregation Group). This setup is typicallyused in multi-homing scenarios to provide redundancy and load balancing across multiple physical links.
Conclusion:
* Option A:Correct-The host with MAC 40:00:dc:01:00:04 is assigned IP 10.4.4.5.
* Option D:Correct-The host is originating from an ESI LAG, as indicated by the active source value.
NEW QUESTION # 55
Which two statements are true about IP fabrics using unnumbered BGP? (Choose two.)
- A. Unnumbered BGP peering automatically provisions IPv6 peering.
- B. Unnumbered BGP requires that family inet is configured on each interface.
- C. Unnumbered BGP peering automatically provisions IPv4 peering.
- D. Unnumbered BGP requires that family inet6is configured on each interface.
Answer: B,C
Explanation:
* Understanding Unnumbered BGP:
* Unnumbered BGP (Border Gateway Protocol) allows BGP peering between routers without assigning specific IP addresses to the interfaces. Instead, it uses the loopback address or another router identifier for the BGP session, making IP address management more straightforward in large-scale networks.
* Family inet Configuration:
* Option C:The family inet configuration is required on each interface involved in unnumbered BGP peering to support IPv4 address families. This ensures that IPv4 peering sessions can be established between devices.
* Automatic IPv4 Peering:
* Option D:Unnumbered BGP peering automatically provisions IPv4 peering sessions. This simplifies the configuration by eliminating the need to manually assign and manage IP addresses for BGP peering.
Conclusion:
* Option C:Correct-Unnumbered BGP requires the family inet configuration for IPv4.
* Option D:Correct-Unnumbered BGP automatically provisions IPv4 peering, simplifying setup.
NEW QUESTION # 56
In your EVPN-VXAN environment, you want to prevent a multihomed server from receiving multiple copies ofBUM traffic in active/active scenarios. Which EVPN route type would satisfy this requirement?
- A. Type 7
- B. Type 4
- C. Type 5
- D. Type 8
Answer: B
Explanation:
* Understanding the Scenario:
* In an EVPN-VXLAN environment, when using multi-homing in active/active scenarios, there's a risk that a multihomed server might receive duplicate copies of Broadcast, Unknown unicast, and Multicast (BUM) traffic. This is because multiple VTEPs might forward the same BUM traffic to the server.
* EVPN Route Types:
* Type 4 Route (Ethernet Segment Route):This route type is used to advertise the Ethernet Segment (ES) to which the device is connected. It is specifically used in multi-homing scenarios to signal the ES and its associated Ethernet Tag to all the remote VTEPs. The Type 4 route includes information that helps prevent BUM traffic duplication in active/active multi-homing by using a split-horizon mechanism, which ensures that traffic sent to a multihomed device does not get looped back.
* Explanation:
* The Type 4 route is crucial for ensuring that in a multi-homed setup, particularly in an active
/active configuration, BUM traffic does not result in duplication at the server. The route helps coordinate which VTEP is responsible for forwarding the BUM traffic to the server, thereby preventing duplicate traffic.
Data Center References:
* Type 4 routes are essential for managing multi-homing in EVPN to avoid the issues of BUM traffic duplication, which could otherwise lead to inefficiencies and potential network issues.
NEW QUESTION # 57
Which two statements are correct about an IP fabric? (Choose two.)
- A. All leaf devices can use the same AS number in an IP fabric without making any adjustments to the EBGP configuration
- B. Only a single point to point EBGP session is required between peers in an IP fabric.
- C. The multipath multiple-as statement is required to enable ECMP if every device has a different AS number.
- D. FBGP is only required to route mostrouting information to external devices outside the fabric.
Answer: A,C
Explanation:
* BGP in IP Fabric:
* In an IP fabric, Border Gateway Protocol (BGP) is used to manage the routing between leaf and spine devices. Each device can have the same or different Autonomous System (AS) numbers depending on the network design.
* Multipath Multiple-AS:
* Option B:If every device in the fabric has a different AS number, then enabling Equal-Cost Multi-Path (ECMP) routing requires the multipath multiple-as statement. This configuration allows BGP to consider multiple paths across different AS numbers as equal cost, enabling efficient load balancing across the network.
* Same AS Number Configuration:
* Option A:It's possible for all leaf devices to use the same AS number in an IP fabric, which simplifies the configuration. EBGP (External BGP) will still function correctly in this setup because BGP considers the peering relationship rather than strictly enforcing different AS numbers in this specific use case.
Conclusion:
* Option B:Correct-This statement is essential for enabling ECMP in a multi-AS environment.
* Option A:Correct-Leaf devices can share the same AS number without needing special EBGP configuration.
NEW QUESTION # 58
You are deploying a Clos IP fabric with an oversubscription ratio of 3:1.
In this scenario, which two statements are correct? (Choose two.)
- A. The oversubscription ratio increases when you remove spine devices.
- B. The oversubscription ratio decreases when you add spine devices.
- C. The oversubscription ratio remains the same when you remove spine devices.
- D. The oversubscription ratio remains the same when you add spine devices.
Answer: A,B
Explanation:
* Understanding Oversubscription in a Clos Fabric:
* The oversubscription ratio in a Clos IP fabric measures the ratio of the amount of edge (leaf) bandwidth to the core (spine) bandwidth. An oversubscription ratio of 3:1 means that there is three times more edge bandwidth compared to core bandwidth.
* Impact of Adding/Removing Spine Devices:
* Option C:If youremove spine devices, the total available core bandwidth decreases, while the edge bandwidth remains the same. This results in anincrease in the oversubscription ratio because there is now less core bandwidth to handle the same amount of edge traffic.
* Option B:Conversely, if youadd spine devices, the total core bandwidth increases. This decreases the oversubscription ratio because more core bandwidth is available to handle the edge traffic.
Conclusion:
* Option C:Correct-Removing spine devices increases the oversubscription ratio.
* Option B:Correct-Adding spine devices decreases the oversubscription ratio.
NEW QUESTION # 59
......
Juniper JN0-683 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
Share Latest JN0-683 DUMP Questions and Answers: https://www.validbraindumps.com/JN0-683-exam-prep.html
JN0-683 Questions and Answers Guarantee you Oass the Test Easily: https://drive.google.com/open?id=1FmwWHjk5XokjGM45jUjvu7kK3UN42OsT