

[Jun 30, 2026] JN0-683 Practice Exam Dumps - 99% Marks In Juniper Exam
Updated Verified JN0-683 Q&As - Pass Guarantee or Full Refund
Juniper JN0-683 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
NEW QUESTION # 28
You are deploying an IP fabric using EBGP and notice that your leaf devices areadvertising and receiving all the routes. However, the routes are not installed in the routing table and are marked as hidden.
Which two statements describe how to solve the issue? (Choose two.)
- A. You need to configure loops 2.
- B. You need to configure as-override.
- C. You need to configure multipath multiple-as.
- D. You need to configure a next-hop self policy.
Answer: C,D
NEW QUESTION # 29
Referring to the exhibit, which statement is correct?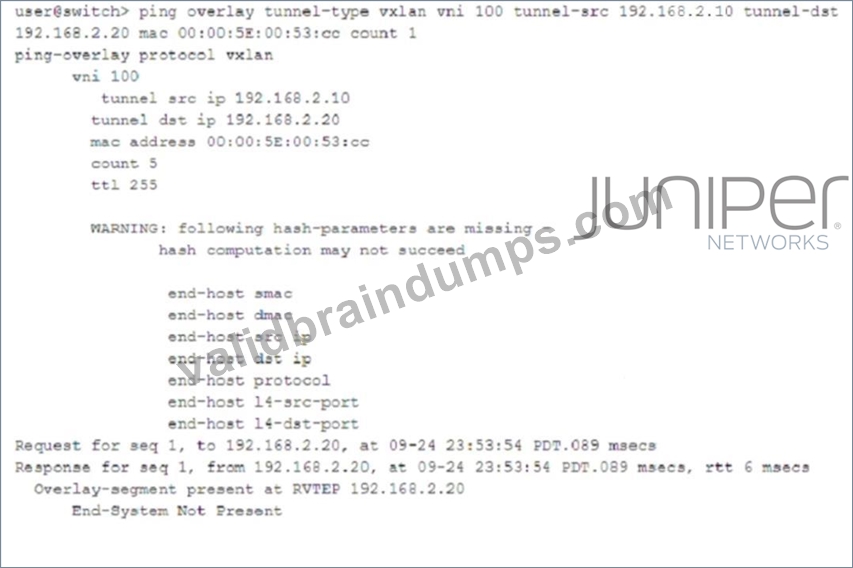
- A. The MAC address is unknown and not in the forwarding table of the remote VTEP.
- B. VNI 100 is not configured on the remote VTEP.
- C. The MAC address is known but not reachable by the remote VTEP.
- D. The remote VTEP is not responding.
Answer: A
Explanation:
The output shows a VXLAN ping test using ping overlayto verify VXLAN reachability between VTEPs (Virtual Tunnel Endpoints). The test successfully reaches the remote VTEP
192.168.2.20, meaning the VXLAN tunnel is functional. However, the response indicates "End- System Not Present," which means that while the VXLAN segment is active on the remote VTEP, the specified MAC address (00:00:5E:00:53:CC) is not known in the forwarding table of the remote VTEP.
NEW QUESTION # 30
A local VTEP has two ECMP paths to a remote VTEP
Which two statements are correctwhen load balancing is enabled in this scenario? (Choose two.)
- A. The inner packet fields are not used in the hash for load balancing.
- B. The destination port in the UDP header is used to load balance VXLAN traffic.
- C. The source port in the UDP header is used to load balance VXLAN traffic.
- D. The inner packet fields are used in the hash for load balancing.
Answer: C,D
Explanation:
* Load Balancing in VXLAN:
* VXLAN uses UDP encapsulation to transport Layer 2 frames over an IP network. For load balancing across Equal-Cost Multi-Path (ECMP) links, various fields in the packet can be used to ensure even distribution of traffic.
* Key Load Balancing Fields:
* C. The source port in the UDP header is used to load balance VXLAN traffic:This is correct.
The source UDP port in the VXLAN packet is typically calculated based on a hash of the inner packet's fields. This makes the source port vary between packets, enabling effective load balancing across multiple paths.
* D. The inner packet fields are used in the hash for load balancing:This is also correct. Fields such as the source and destination IP addresses, source and destination MACaddresses, and possibly even higher-layer protocol information from the inner packet can be used to generate the hash that determines the ECMP path.
* Incorrect Statements:
* A. The inner packet fields are not used in the hash for load balancing:This is incorrect as the inner packet fields are indeed critical for generating the hash used in load balancing.
* B. The destination port in the UDP header is used to load balance VXLAN traffic:This is incorrect because the destination UDP port in VXLAN packets is typically fixed (e.g., port 4789 for VXLAN), and therefore cannot be used for effective load balancing.
Data Center References:
* Effective load balancing in VXLAN is crucial for ensuring high throughput and avoiding congestion on specific links. By using a combination of the source UDP port and inner packet fields, the network can distribute traffic evenly across available paths.
NEW QUESTION # 31
You are deploying a new network to support your AI workloads on devices that support at least
400 Gbps Ethernet. There is no requirement for any Layer 2 VLANs in this network.
Which network architecture would satisfy this requirement?
- A. an IP fabric using EBGP
- B. an IP fabric using PIM-SM to signal VXLAN overlay
- C. an IP fabric with an EVPN-VXLAN architecture
- D. an IP fabric using the EVPN-MPLS architecture
Answer: A
Explanation:
For high-performance AI workloads requiring speeds of 400 Gbps or more, a pure Layer 3 IP fabric using EBGP underlay routing is typically deployed for scalability and efficiency. This avoids the complexities of Layer 2 VLANs and minimizes oversubscription.
EBGP-based IP fabrics are common in modern data centers to provide large-scale, scalable, and high-bandwidth connectivity between leaves and spines with VXLAN or other overlays as appropriate but without mandatory Layer 2 VLANs.
EBGP-based IP fabrics typically provide a pure Layer 3 routing underlay that scales easily with high port speeds such as 400Gbps.
NEW QUESTION # 32
You are deploying an IP fabric using EBGP and notice that your leaf devices areadvertising and receiving all the routes. However, the routes are not installed in the routing table and are marked as hidden.
Which two statements describe how to solve the issue? (Choose two.)
- A. You need to configure loops 2.
- B. You need to configure as-override.
- C. You need to configure multipath multiple-as.
- D. You need to configure a next-hop self policy.
Answer: C,D
Explanation:
* Issue Overview:
* The leaf devices in an IP fabric using eBGP are advertising and receiving all routes, but the routes are not being installed in the routing table and are marked as hidden. Thistypically indicates an issue with the BGP configuration, particularly with next-hop handling or AS path concerns.
* Corrective Actions:
* B. You need to configure a next-hop self policy:This action ensures that the leaf devices modify the next-hop attribute to their own IP address before advertising routes to their peers. This is particularly important in eBGP setups where the next-hop may not be directly reachable by other peers.
* D. You need to configure multipath multiple-as:This setting allows the router to accept multiple paths from different autonomous systems (ASes) and use them for load balancing.
Without this, the BGP process might consider only one path and mark others as hidden.
* Incorrect Statements:
* A. You need to configure as-override:AS-override is used to replace the AS number in the AS- path attribute to prevent loop detection issues in MPLS VPNs, not in a typical eBGP IP fabric setup.
* C. You need to configure loops 2:There is no specific BGP command loops 2 relevant to resolving hidden routes in this context. It might be confused with allowas-in, which is used to allow AS path loops under certain conditions.
Data Center References:
* Proper BGP configuration is crucial in IP fabrics to ensure route propagation and to prevent routes from being marked as hidden. Configuration parameters like next-hop self and multipath multiple-as are common solutions to ensure optimal route installation and load balancing in a multi-vendor environment.
NEW QUESTION # 33
You are using a single tenant data center with a bridged overlay architecture. In this scenario, how do hosts of the different virtual networks communicate with each other?
- A. using anycast gateway addresses configured on the leaf devices
- B. using virtual gateway addresses configured on the spine
- C. off-fabric using an external device
- D. using EVPN Type 5 routes
Answer: C
Explanation:
In a single-tenant data center using a bridged overlay architecture, virtual networks (VLANs) are typically isolated within the fabric, with traffic between these VLANs handled outside the fabric.
off-fabric using an external device: In many bridged overlay architectures, communication between different virtual networks is handled off-fabric, often using an external router or firewall that connects the different VLANs. The fabric itself primarily provides Layer 2 connectivity within each VLAN, leaving inter-VLAN routing to be handled externally.
This design is common in smaller or simpler data center environments where a single tenant does not require complex on-fabric routing and prefers to handle inter-VLAN routing through dedicated devices.
NEW QUESTION # 34
Which two statements are true about IP fabrics using unnumbered BGP? (Choose two.)
- A. Unnumbered BGP requires that family inet is configured on each interface.
- B. Unnumbered BGP peering automatically provisions IPv4 peering.
- C. Unnumbered BGP requires that family inet6 is configured on each interface.
- D. Unnumbered BGP peering automatically provisions IPv6 peering.
Answer: C,D
Explanation:
BGP unnumbered peering uses only link-local IPv6 addresses on interfaces to automatically discover and establish BGP peer sessions. No routable IP addresses are required on the underlay interfaces.
You must configure the interfaces with family inet6 to enable the link-local IPv6 addresses used for peering.
The BGP peering session is dynamically created based on interface names, which simplifies the configuration significantly compared to manual peering with routable IP addresses.
The peer IP and remote AS numbers are automatically configured for BGP unnumbered peering.
This means unnumbered BGP automatically provisions IPv6 peering using the link-local addresses.
It also supports IPv4 route exchange over the IPv6 next-hop established by unnumbered BGP.
https://www.juniper.net/documentation/us/en/software/nce/nce-225-bgp-unnumbered/index.html
NEW QUESTION # 35
Exhibit.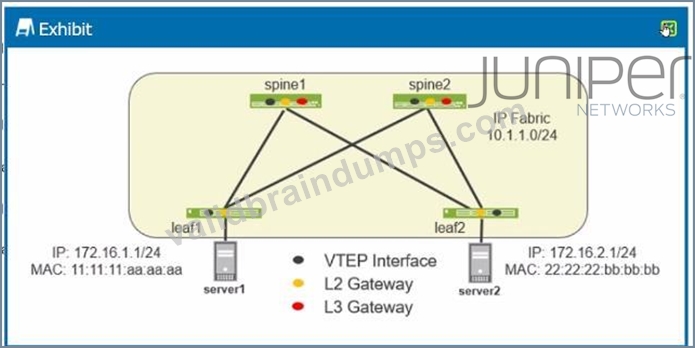
You have implemented an EVPN-VXLAN data center. Device served must be able to communicate with device server2.
Referring to the exhibit, which two statements are correct? (Choose two.)
- A. An IRB interface must be configured on spinel and spine2.
- B. Traffic from server! to server2 will transit the VXLAN tunnel between leaf1 and Ieaf2.
- C. An IRB Interface must be configured on leaf1 and Ieaf2.
- D. Traffic from server1 to server2 will transit a VXLAN tunnel to spinel or spine2. then a VXLAN tunnel from spinel or spine2 to Ieaf2.
Answer: B,C
Explanation:
* Understanding the Exhibit Setup:
* The network diagram shows an EVPN-VXLAN setup, a common design for modern data centers enabling Layer 2 and Layer 3 services over an IP fabric.
* Leaf1 and Leaf2 are the leaf switches connected to Server1 and Server2, respectively, with each server in a different subnet (172.16.1.0/24 and 172.16.2.0/24).
* Spine1 and Spine2 are part of the IP fabric, interconnecting the leaf switches.
* EVPN-VXLAN Basics:
* EVPN (Ethernet VPN) provides Layer 2 and Layer 3 VPN services using MP-BGP.
* VXLAN (Virtual Extensible LAN) encapsulates Layer 2 frames into Layer 3 packets for transmission across an IP network.
* VTEP (VXLAN Tunnel Endpoint) interfaces on leaf devices handle VXLAN encapsulation and decapsulation.
* Integrated Routing and Bridging (IRB):
* IRB interfaces are required on leaf1 and leaf2 (where the endpoints are directly connected) to route between different subnets (in this case, between 172.16.1.0/24 and 172.16.2.0/24).
* The IRB interfaces provide the necessary L3 gateway functions for inter-subnet communication.
* Traffic Flow Analysis:
* Traffic from Server1 (172.16.1.1) destined for Server2 (172.16.2.1) must traverse from leaf1 to leaf2.
* The traffic will be VXLAN encapsulated on leaf1, sent over the IP fabric, and decapsulated on leaf2.
* Since the communication is between different subnets, the IRB interfaces on leaf1 and leaf2 are crucial for routing the traffic correctly.
* Correct Statements:
* C. An IRB Interface must be configured on leaf1 and leaf2:This is necessary to perform the inter-subnet routing for traffic between Server1 and Server2.
* D. Traffic from server1 to server2 will transit the VXLAN tunnel between leaf1 and leaf2:
This describes the correct VXLAN operation where the traffic is encapsulated by leaf1 and decapsulated by leaf2.
Data Center References:
* In EVPN-VXLAN architectures, the leaf switches often handle both Layer 2 switching and Layer 3 routing via IRB interfaces. This allows for efficient routing within the data center fabric without the need to involve the spine switches for every routing decision.
* The described traffic flow aligns with standard EVPN-VXLAN designs, where direct VXLAN tunnels between leaf switches enable seamless and scalable communication across a data center network.
NEW QUESTION # 36
You are designing an IP fabricfora large data center, and you are concerned about growth and scalability.
Which two actions would you take to address these concerns? (Choose two.)
- A. Use OFX5700 Series devices as the super spines.
- B. Use EX4300 Series devices as the spine devices.
- C. Design a three-stage Clos IP fabric.
- D. Design a five-stage Clos IP fabric.
Answer: A,D
NEW QUESTION # 37
Which two statements are correct about an IP fabric? (Choose two.)
- A. Only a single point to point EBGP session is required between peers in an IP fabric.
- B. All leaf devices can use the same AS number in an IP fabric without making any adjustments to the EBGP configuration
- C. EBGP is only required to route most routing information to external devices outside the fabric.
- D. The multipath multiple-as statement is required to enable ECMP if every device has a different AS number.
Answer: A,D
Explanation:
When each device in the IP fabric has a different AS number, the BGP "multipath multiple-as" statement must be enabled to allow ECMP (Equal-Cost Multi-Path) across EBGP peers with different ASNs.
EBGP sessions in an IP fabric are established as single point-to-point sessions between directly connected devices, typically leaf-to-spine, allowing for scalable and straightforward peering.
NEW QUESTION # 38
Your organization is implementing EVPN-VXLAN and requires multiple overlapping VLAN-IDs.
You decide to use a routing-instance type mac-vrfto satisfy this request.
Which two statements are correct in this scenario? (Choose two.)
- A. Host-facing interfaces must be configured using a service-provider style configuration.
- B. Spine-facing interfaces must be configured using an enterprise-style configuration.
- C. Host-facing interfaces must be configured using enterprise-style configuration.
- D. The routing-instance service type can be VLAN-based.
Answer: A,D
Explanation:
Host-facing interfaces must be configured using a service-provider style configuration When using MAC-VRF routing instances to support overlapping VLAN IDs, host-facing interfaces need service-provider style (unit with VLAN tagging inside a logical interface). This allows the same VLAN ID to exist in multiple VRFs without conflict.
The routing-instance service type can be VLAN-based
MAC-VRF instances can be VLAN-based, which maps a VLAN to the routing instance for L2 segregation.
NEW QUESTION # 39
You are asked to set up an IP fabric thatsupports Al or ML workloads. You have chosen to use lossless Ethernet in this scenario, which statement is correct about congestion management?
- A. ECN marks packets based on WRED settings.
- B. ECN is negotiated only among the switches that make up the IP fabric for each queue.
- C. Only the source and destination devices need ECN enabled.
- D. The switch experiencing the congestion notifies the source device.
Answer: D
Explanation:
* Understanding Lossless Ethernet and Congestion Management:
* Lossless Ethernet is crucial for AI and ML workloads, where packet loss can significantly degrade performance. To implement lossless Ethernet, congestion management protocols like ECN (Explicit Congestion Notification) are used.
* Role of ECN in Congestion Management:
* Option A:In an IP fabric that supports lossless Ethernet, when a switch experiences congestion, it can mark packets using ECN. This marking notifies the source device of the congestion, allowing the source to reduce its transmission rate, thereby preventing packet loss.
Conclusion:
* Option A:Correct-The switch experiencing congestion notifies the source device via ECN marking.
NEW QUESTION # 40
You manage an IP fabric with an EVPN-VXLAN overlay. You have multiple tenants separated using multiple unique VRF instances. You want to determine the routing information that belongs in each routing instance's routing table.
In this scenario, which property is used for this purpose?
- A. the VRF table label
- B. the VRF target community
- C. the routing instance type
- D. the route distinguisher value
Answer: D
Explanation:
* Understanding VRF and Routing Instances:
* In an EVPN-VXLAN overlay network, multiple tenants are separated using unique VRF (Virtual Routing and Forwarding) instances. Each VRF instance maintains its own routing table, allowing for isolated routing domains within the same network infrastructure.
* Role of Route Distinguisher:
* Route Distinguisher (RD):The RD is a unique identifier used in MPLS and EVPN environments to distinguish routes belonging to different VRFs. The RD is prepended to the IP address in the route advertisement, ensuring that routes from different tenants remain unique even if they use the same IP address range.
* Correct Property:
* D. the route distinguisher value:This is the correct answer because the RD is crucial in determining which routing information belongs to which VRF instance. It ensures that each VRF' s routing table only contains relevant routes, maintaining isolation between tenants.
Data Center References:
* The RD is a key element in MPLS and EVPN-based multi-tenant environments, ensuring proper routing segregation and isolation for different VRFs within the data center fabric.
NEW QUESTION # 41
Exhibit.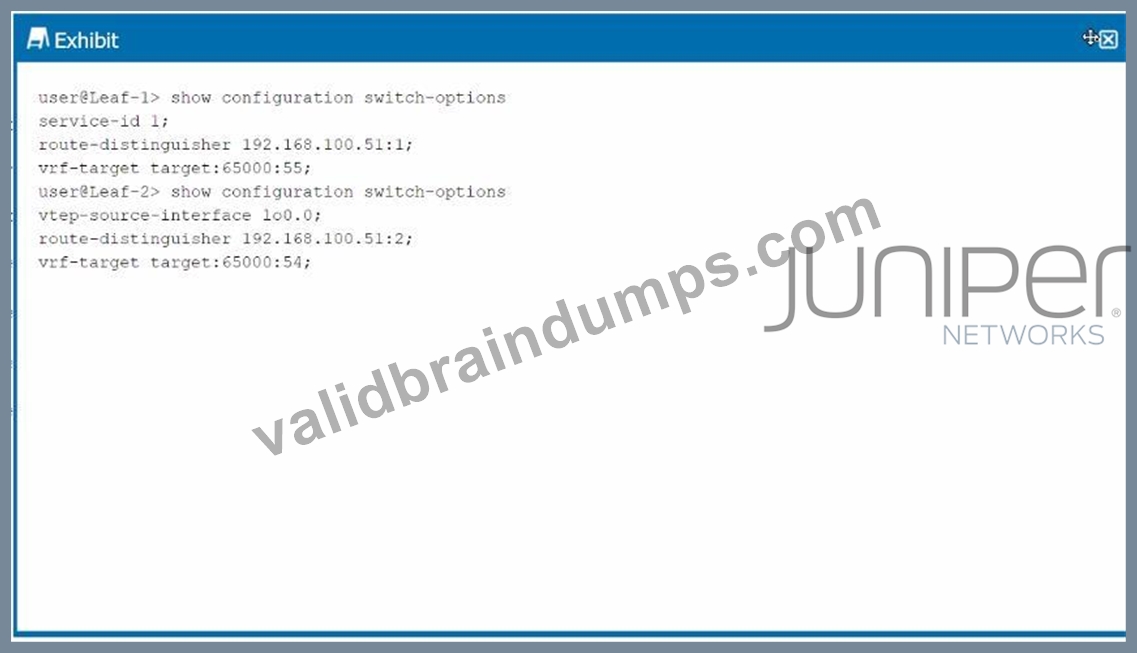
Connections between hosts connected to Leaf-1 and Leaf-2 are not working correctly.
Referring to the exhibit, which two configuration changes are required to solve the problem? (Choose two.)
- A. Configure the set switch-options service-id 1 parameter on Leaf-2.
- B. Configure the setswitch-options route-distinguisher 192.168.100.51:2 parameter on Leaf-1.
- C. Configure the setswitch-options vtep-source-interface100. 0 parameter on Leaf-1.
- D. Configure the set switch-options vrf-target target: 65000:55 parameter on Leaf-2.
Answer: A,D
Explanation:
* Review of the Exhibit:
* The exhibit shows the switch configuration for Leaf-1 and Leaf-2. The configurations include route distinguishers, VRF targets, and service IDs, all of which are crucial for ensuring proper operation in an EVPN-VXLAN environment.
* Service-ID Consistency:
* The service ID must be consistent across all participating leaf devices in the same EVPN instance to ensure that they are part of the same VXLAN overlay network.
* VRF Target Consistency:
* The vrf-target parameter must also be consistent across devices to ensure that VRFs (Virtual Routing and Forwarding instances) are correctly imported and exported between leaf nodes.
Conclusion:
* Option B:Correct-Setting the same service-id on Leaf-2 ensures that it is part of the same VXLAN overlay as Leaf-1.
* Option D:Correct-The vrf-target on Leaf-2 should match Leaf-1 to ensure consistent routing policies and proper route exchange.
NEW QUESTION # 42
You are asked to deploy 100 QFX Series devices using ZTP. Each QFX5120 requires a different configuration.
In this scenario, what are two components that you would configure on the DHCP server?
(Choose two.)
- A. the MAC address of the FTP server
- B. the IP address of the FTP server
- C. the management IP address for each QFX5120
- D. the MAC address for each QFX5120
Answer: B,C
Explanation:
The IP address of the FTP server: In a Zero Touch Provisioning (ZTP) deployment, the DHCP server needs to provide the IP address of a server (such as an FTP or TFTP server) that holds the configuration files or software images required for the device. The QFX devices will reach out to this server during the boot process to download their necessary configuration and images.
The management IP address for each QFX5120: The DHCP server should also provide the management IP address for each QFX5120, allowing the devices to connect to the network and communicate with the ZTP server for configuration.
NEW QUESTION # 43
You are asked to set up an IP fabric that supports AI or ML workloads. You have chosen to use lossless Ethernet.
In this scenario, which statement is correct about congestion management?
- A. ECN marks packets based on WRED settings.
- B. ECN is negotiated only among the switches that make up the IP fabric for each queue.
- C. Only the source and destination devices need ECN enabled.
- D. The switch experiencing the congestion notifies the source device.
Answer: D
Explanation:
In a lossless Ethernet environment, such as one designed to support AI or ML workloads, ECN (Explicit Congestion Notification) is used to signal congestion to the source device. When congestion occurs in the network, the switch experiencing the congestion marks packets with ECN to notify the source device. This allows the source to adjust its sending rate, helping to avoid further congestion and ensuring that traffic continues to flow efficiently.
NEW QUESTION # 44
Which parameter is used to associate a received route with a local VPN route table?
- A. route-target community
- B. VLAN ID
- C. VNI
- D. route-distinguisher
Answer: A
Explanation:
* Understanding VPN Route Table Association:
* In MPLS/VPN and EVPN networks, theroute-target communityis a BGP extended community attribute used to control the import and export of VPN routes. It associates received routes with the appropriate VPN route tables on the PE (Provider Edge) routers.
* Function of Route-Target Community:
* The route-target community tag ensures that routes are imported into the correct VRF (Virtual Routing and Forwarding) instance, allowing them to be correctly routed within the VPN.
Conclusion:
* Option A:Correct-The route-target community is used to associate received routes with a local VPN route table.
NEW QUESTION # 45
You are deploying an IP fabric using EBGP and notice that your leaf devices are advertising and receiving all the routes. However, the routes are not installed in the routing table and are marked as hidden.
Which two statements describe how to solve the issue? (Choose two.)
- A. You need to configure multipath multiple-as.
- B. You need to configure loops 2.
- C. You need to configure as-override.
- D. You need to configure a next-hop self policy.
Answer: B,D
Explanation:
You need to configure a next-hop self policy: When using EBGP, the next-hop IP address in the routing advertisements might not be reachable from the receiving device, causing the routes to be marked as hidden. By configuring the next-hop-selfpolicy, the leaf devices will change the next-hop IP to their own IP address for the routes they advertise, making them reachable within the fabric and allowing the routes to be installed in the routing table.
You need to configure loops 2: When all leaves share the same AS (common-AS design), BGP loop prevention drops routes learned from the same AS. Configuring loops 2 allows the leaf to accept routes with its own AS in the path twice, which is needed in an eBGP IP fabric with repeated AS numbers.
NEW QUESTION # 46
You are asked to build out the VXLAN control plane.
In this scenario, which two protocols provide this capability? (Choose two.)
- A. MBGP
- B. IS-IS
- C. PIM-SM
- D. OSPF
Answer: A,C
Explanation:
MBGP (Multicast BGP): MBGP is used to advertise VXLAN information across the control plane, specifically for multicast-based VXLAN deployment. It helps in distributing VXLAN Network Identifiers (VNIs) and other relevant information in an efficient manner across the network.
PIM-SM (Protocol Independent Multicast - Sparse Mode): PIM-SM is used to build multicast distribution trees in VXLAN flood-and-learn mode or when multicast-based VXLAN control planes are used.
NEW QUESTION # 47
Exhibit.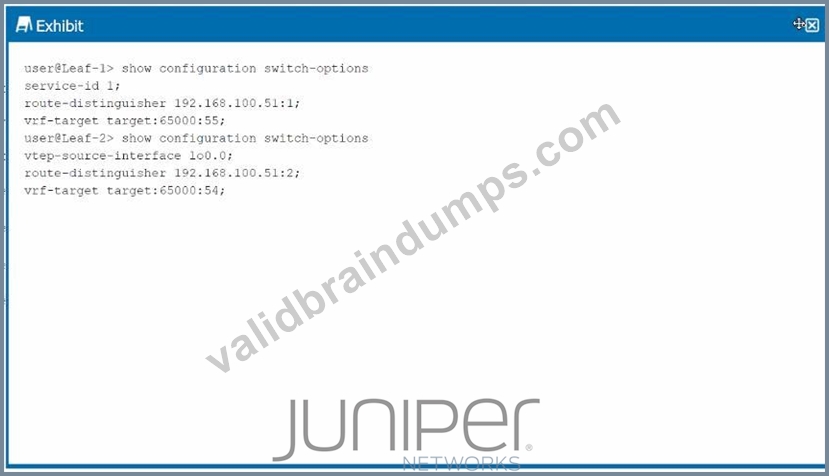
Connections between hosts connected to Leaf-1 and Leaf-2 are not working correctly.
Referring to the exhibit, which two configuration changes are required to solve the problem? (Choose two.)
- A. Configure the set switch-options service-id 1 parameter on Leaf-2.
- B. Configure the set switch-options vtep-source-interface 100. 0 parameter on Leaf-1.
- C. Configure the set switch-options vrf-target target: 65000:55 parameter on Leaf-2.
- D. Configure the set switch-options route-distinguisher 192.168.100.51:2 parameter on Leaf-1.
Answer: A,C
Explanation:
* Review of the Exhibit:
* The exhibit shows the switch configuration for Leaf-1 and Leaf-2. The configurations include route distinguishers, VRF targets, and service IDs, all of which are crucial for ensuring proper operation in an EVPN-VXLAN environment.
* Service-ID Consistency:
* The service ID must be consistent across all participating leaf devices in the same EVPN instance to ensure that they are part of the same VXLAN overlay network.
* VRF Target Consistency:
* The vrf-target parameter must also be consistent across devices to ensure that VRFs (Virtual Routing and Forwarding instances) are correctly imported and exported between leaf nodes.
Conclusion:
* Option B:Correct-Setting the same service-id on Leaf-2 ensures that it is part of the same VXLAN overlay as Leaf-1.
* Option D:Correct-The vrf-target on Leaf-2 should match Leaf-1 to ensure consistent routing policies and proper route exchange.
NEW QUESTION # 48
......
JN0-683 Real Valid Brain Dumps With 70 Questions: https://www.validbraindumps.com/JN0-683-exam-prep.html
JN0-683 Certification with Actual Questions: https://drive.google.com/open?id=1FmwWHjk5XokjGM45jUjvu7kK3UN42OsT